Working in IT for the U.S. DoD

Step into the world of U.S. DoD IT roles. Equip yourself with the knowledge of pivotal DoD Directives and achieve the certifications that set you apart.

DoD Directives 8570, 8570.01-M, and 8140

If you’re interested in working in any technology-related role for the U.S. Department of Defense, you are required per Directive 8140 (which replaced Directive 8570) to obtain and maintain industry certification credentials that have been accredited by the American National Standards Institute (ANSI). This is true for everyone (both civilians and those still serving in the military) who will have privileged access to DoD’s Information Systems.

CCS Learning Academy offers qualified certificate courses from accreditors like CompTIA, (ISC)2, and more! Veterans can work with us to get the credentials they need to be hired for DoD cybersecurity jobs. We can also help individuals obtain the continuing education credits necessary to maintain their existing certifications.
cybersecurity_screen-min

73 %

of workers say that the top benefit of certification is credibility.

57 %

of workers say a certification will help them advance in their current job.

56 %

of workers say a certification will improve their chances for a new position.

In recent CompTIA research, the large majority of IT and business executives involved in security indicated that IT staff certification has made a difference.

CCS Learning Academy

CCS Learning Academy Logo

Trusted experts in the technology sector since 1997

IT & business training for professionals at all levels

A network of trainers and clients spanning the entire U.S.

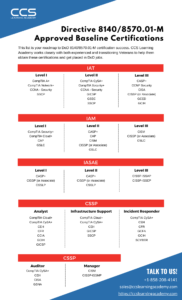
Certifications Approved for DoD Directive 8140/8570.01-M

DoD Directive 8140 is a replacement on and expansion of Directive 8570, which was first released in 2005 to help the DoD manage and audit its cybersecurity personnel. Since then, both the world and technology have changed – a lot! DoD 8140 is the result of several important decisions made to better reflect today’s tech landscape and job market.

Among other updates to DoD 8570, DoD 8140 covers the following:

  • Updates and expansions on DoD policies, processes, and responsibilities around managing its cybersecurity workforce.
  • The establishment of a DoD cyberspace workforce management council.
  • Unification and alignment of technology work roles with regard to baseline qualifications and training requirements.

DoD technology jobs are an excellent fit for many Veterans, as their experiences and clearances translate into distinct advantages in this environment. CCS Learning Academy can help you understand what career pathways are available, what certifications you will need along the way, and how to launch a successful IT career at the U.S. DoD.

DoD-8140_8570.01

Download this guide to see the complete roadmap to success for aspiring DoD technology professionals per Directive 8140/8570.01-M.

More CompTIA Certifications Now Approved for Directive 8140/8570.01-M!

CompTIA is proud to be the leading choice in certifications for DoD personnel and contractors, helping hundreds of thousands of servicemen, servicewomen, and DoD civilians to meet their Directive 8140/8570 requirements. CompTIA certifications also serve as the building blocks for more advanced certifications; for example, CompTIA Network+ and Security+ are accepted as prerequisites to the Microsoft Software & Systems Academy training course.

CompTIA_badge_aplus-min-150x150

CompTIA A+

This credential validates the foundational knowledge for IT Technical Support. It’s recognized as the standard for foundation-level IT knowledge and skills, including installing, configuring, diagnosing and preventive maintenance of hardware and software components, as well as networks and soft skills.

CompTIA_badge_networkplus-min-150x150

CompTIA Network+

This credential validates the knowledge of networking professionals with at least 9-12 months of experience in network support or administration or adequate academic training. Many corporations recommend or require this certification for their IT employees; it is one of CompTIA’s core certifications.
CompTIA_badge_securityplus-min-150x150

CompTIA Security+

This credenttial validates mastery of security knowledge for an individual with two years of on-the-job networking experience, with emphasis on security. The exam covers threats, attacks, and vulnerabilities; technologies and tools; architecture and design; identity and access management; risk management; and cryptography and PKI.

CompTIA_badge_cloudplus-min-150x150

CompTIA Cloud+

Approved for three 8140/8570 job roles, this certification validates the expertise needed to maintain and optimize cloud infrastructure services. IT professionals with a Cloud+ certification can better realize the return on investment of cloud infrastructure services. Cloud+ reflects the breadth of skills needed for data center job roles.

CompTIA_badge_cysaplus-min-150x150

CompTIA CySA+

Approved for five 8140/8570 job roles, this is designed for IT security analysts as well as vulnerability and threat intelligence analysts. The successful candidate has the knowledge and skills required to configure and use threat detection tools, perform data analysis, and interpret the results to identify vulnerabilities, threats, and risks to an organization.

CompTIA_badge_caspplus-min-150x150

CompTIA CASP+

This certification is designed to meet the growing demand for advanced IT security in the enterprise. It tests critical thinking and judgment across a broad spectrum of security disciplines and requires candidates to implement clear solutions in complex environments. The exam covers enterprise security, risk management and incident response, research and analysis, integration of computing, and communications and business disciplines as well as technical integration of enterprise components.

Why choose CCS Learning Academy?

CCS Learning Academy is one of the industry’s top CompTIA training partners, and we have a team dedicated to working exclusively with transitioning and experienced Veterans. We are honored to assist U.S. service members in transitioning from active duty to high-paying careers in the civilian IT workforce.

Your future is waiting.

Start the next phase of your career today!

Certifications Approved for DoD Directive 8570.01

While DoD Directive 8140 was issued to update and replace DoD 8570, the older Directive 8570 (technically, 8570.01) is still around. It may take a long time to issue a comprehensive manual covering the 8140 security requirements, which is why DoD 8140 still refers to the DoD 8570 manual (“DoD 8570.01-M”).

Like its successor, DoD 8570 requires all users of DoD information systems to meet certain compliance requirements. These requirements include holding certifications accredited by the American National Standards Institute (ANSI). Per the Directive, there are three levels of certification for Information Assurance Technicians (IAT) and Information Assurance Management (IAM) professionals. Anyone wishing to hold these kinds of positions at the U.S. DoD must obtain at least one of the certifications required for the relevant job level.

DoD-8570.01

Download this guide to see the full list of approved baseline certifications per DoD Directive 8570.01.

DoD 8140, 8570.01-M, and 8570-Approved Courses from CCS Learning Academy

CSSLP – Certified Secure Software Lifecycle Professional

40 hours
All Levels
What you'll learn
The course on CSSLP teaches how to secure your applications. After having CSSLP certification from (ISC) ², your application security capability within the software development lifecycle will be authorized. In-depth coverage of the eight domains required to pass the CSSLP exam.
Domain 1: Secure Software Concepts
Domain 2: Security Software Requirements
Domain 3: Secure Software Design
Domain 4: Secure Software Implementation/Coding
Domain 5: Secure Software Testing
Domain 6: Software Acceptance
Domain 7: Software Deployment, Operation, Maintenance and Disposal
Domain 8: Supply Chain and Software Acquisition

ISO/IEC 27032 Lead Cybersecurity Manager

5 Lessons
40 hours
Intermediate
What you'll learn
Acquire comprehensive knowledge on the elements and operations of a Cybersecurity Program in conformance with ISO/IEC 27032 and NIST Cybersecurity framework
Acknowledge the correlation between ISO 27032, NIST Cybersecurity framework and other standards and operating frameworks
Master the concepts, approaches, standards, methods and techniques used to effectively set up, implement, and manage a Cybersecurity program within an organization
Learn how to interpret the guidelines of ISO/IEC 27032 in the specific context of an organization
Master the necessary expertise to plan, implement, manage, control and maintain a Cybersecurity Program as specified in ISO/IEC 27032 and NIST Cybersecurity framework
Acquire the necessary expertise to advise an organization on the best practices for managing Cybersecurity

ISO/IEC 27005 Lead Risk Manager

5 Lessons
40 hours
Intermediate
What you'll learn
Master the concepts, approaches, methods and techniques that enable an effective risk management process based on ISO/IEC 27005
Acknowledge the correlation between Information Security risk management and security controls
Learn how to interpret the requirements of ISO/IEC 27001 in Information Security Risk Management
Acquire the competence and skills to effectively advise organizations on Information Security Risk Management best practices
Acquire the knowledge necessary for the implementation, management and maintenance of an ongoing risk management program

ISO 9001 Lead Implementer

5 Lessons
40 hours
Intermediate
What you'll learn
Acknowledge the correlation between ISO 9001 and other standards and regulatory frameworks
Master the concepts, approaches, methods and techniques used for the implementation and effective management of a QMS
Learn how to interpret the ISO 9001 requirements in the specific context of an organization
Learn how to support an organization to effectively plan, implement, manage, monitor and maintain a QMS
Acquire the expertise to advise an organization in implementing Quality Management System best practices

ISO/IEC 27035 Lead Incident Manager

5 Lessons
40 hours
Intermediate
What you'll learn
Master the concepts, approaches, methods, tools and techniques that enable an effective Information Security Incident Management according to ISO/IEC 27035
Acknowledge the correlation between ISO/IEC 27035 and other standards and regulatory frameworks
Acquire the expertise to support an organization to effectively implement, manage and maintain an Information Security Incident Response plan
Acquire the competence to effectively advise organizations on the best practices of Information Security Incident Management
Understand the importance of establishing well-structured procedures and policies for Incident Management processes
Develop the expertise to manage an effective Incident Response Team

ISO/IEC 27701 Lead Implementer

5 Lessons
40 hours
Intermediate
What you'll learn
Master the concepts, approaches, methods and techniques used for the implementation and effective management of a PIMS.
Learn about the correlation between ISO/IEC 27701, ISO/IEC 27001, ISO/IEC 27002 and other standards and regulatory frameworks.
Understand the operation of a PIMS based on ISO/IEC 27701 and its principal processes.
Learn how to interpret the requirements of ISO/IEC 27701 in the specific context of an organization.
Develop the expertise to support an organization in effectively planning, implementing, managing, monitoring and maintaining a PIMS.

CyberSec First Responder® (CFR)

41 Lessons
40 hours
Intermediate
What you'll learn
Compare and contrast various threats and classify threat profile
Explain the purpose and use of attack tools and technique
Explain the purpose and use of post exploitation tools and tactic
Explain the purpose and use of social engineering tactic
Given a scenario, perform ongoing threat landscape research and use data to prepare for incident
Explain the purpose and characteristics of various data source Given a scenario, use appropriate tools to analyze log
Given a scenario, use regular expressions to parse log files and locate   meaningful data
Given a scenario, use Windows tools to analyze incidents
Given a scenario, use Linux-based tools to analyze incidents
Summarize methods and tools used for malware analysis
Given a scenario, analyze common indicators of potential compromise
Explain the importance of best practices in preparation for incident response
Given a scenario, execute incident response process
Explain the importance of concepts that are unique to forensic analysis
Explain general mitigation methods and devices

“ To say CCS helped me jumpstart my career is an understatement. CCS helps fresh graduates start their professional journey. They provide comprehensive training both technically and professionally that not only prepares you for a full-time job but also helps make you successful in other aspects of your life.”

– Santosh Gadila
Senior IT Analyst
U.S. Department of Veteran Affairs

Get Certified for IT Jobs at the U.S. DoD

Call us at (858) 208-4141 or fill out the form below to get in touch with CCS Learning Academy’s Veteran team.
Upload Your Resume
(if applicable)

File(s) size limit is 20MB.