The internet can be a dangerous place. Like venturing into the Wild West, you never know when bandits might jump out to steal your data or wreak havoc on your computer systems. That’s why every business needs a cybersecurity sheriff to help keep the bad guys at bay.
One of the most trusted deputies in any cybersecurity posse is a powerful piece of software called Nessus. But what is Nessus, and how does it help protect your data?
Nessus rides into your computer systems and scours the premises for vulnerabilities that outlaws could exploit. It locates weaknesses in your defenses and reports back so you can shore up security before the black hats ride into town.
With its advanced scanning techniques, Nessus will sniff out dangers that other cybersecurity scanners would miss. It’s a vital ally for any business hoping to avoid a Cybersecurity O.K. Corral.
In this article, we will explore what exactly Nessus is, how it functions, its key features and capabilities, and why it has become an essential component of cybersecurity strategy for many organizations.
What is Nessus in Cyber Security?
Nessus is a comprehensive vulnerability scanning system developed by Tenable Network Security. Since its initial release in 1998, it has become one of the most popular vulnerability assessment tools used by businesses, government agencies, and security analysts worldwide.
The power of Nessus lies in its ability to automatically detect vulnerabilities and configuration issues in computers, servers, and network devices. It does this by running a series of scans and tests on target systems to identify potential weaknesses that could be exploited by attackers. These tests range from looking for missing security patches and outdated software to checking for weak passwords and improperly configured services.
Key Features of Nessus
Let’s explore its array of features that make it a true champion in the world of cybersecurity.
- Vulnerability Scanning: Nessus can scan networks, operating systems, web applications, databases, and virtual environments to identify vulnerabilities and misconfigurations. It has an extensive database of vulnerability checks and can detect a wide range of issues related to outdated software, default passwords, missing patches, insecure configurations, etc.
- Asset Discovery: Nessus can automatically discover assets and inventory systems connected to a network. It fingerprints operating systems, applications, open ports, and services running on networked devices. This helps identify rogue or forgotten systems.
- Network Scanning: Nessus can map network topology and scan large networks for vulnerabilities efficiently. It can perform host discovery, port scanning, and service enumeration to create an inventory of all assets and attack surfaces.
- Vulnerability Assessment: Nessus assesses vulnerabilities based on threat contexts like exploitability, prevalence, and severity. It provides remediation guidance, verifies if vulnerabilities are fixed after patching, and generates customizable reports.
- Prioritization: Nessus uses patented predictive algorithms to prioritize the most critical risks and vulnerabilities. This allows security teams to focus on fixing high-severity flaws first.
- Policy Management: Nessus allows the creation of customized assessment policies based on the organization’s requirements and objectives. Policies can be assigned to different scans for consistency.
- Web Scanning: Nessus can scan web applications and APIs for vulnerabilities like SQL injection, cross-site scripting, insecure configurations, etc. It can crawl links to cover entire websites and optimize web scanning.

Benefits of Nessus
As you navigate the perilous waters of network vulnerability scanning, it’s essential to understand why Nessus stands head and shoulders above the rest. Let’s explore the key advantages that set Nessus apart.
- Does not make assumptions about server configuration: Nessus does not make any assumptions about the services running on a server or the ports they use. This allows it to find vulnerabilities that other scanners may miss if they assume a particular service is running on a standard port.
- Highly extensible: Nessus provides a plugin architecture and scripting language called NASL. This allows security professionals to write custom plugins and scripts to check for vulnerabilities specific to their environment. There is also a large library of free community-contributed plugins available.
- Up-to-date vulnerability information: The Nessus vulnerability database is updated daily to detect new vulnerabilities and exploits as soon as they emerge. This minimizes the window of exposure to new threats.
- Open source: Nessus is open-source software, so it is free to use, and the source code is publicly available. Users can inspect the code and make modifications if desired.
- Patching assistance: When a vulnerability is detected, Nessus provides detailed information and recommends ways to remediate or patch the issue. This helps administrators fix problems and improve their security posture.
How Does Nessus Work?
Nessus is a vulnerability scanner that uses port scanning to test a computer or network’s security. Port scanning works by sending requests to a range of ports on a remote system and analyzing the responses to determine what services are running and listening on those ports.
Some key points about how Nessus performs port scanning:
- Nessus contains a database of thousands of known vulnerabilities and security holes in various services and applications. This is constantly updated as new vulnerabilities are discovered.
- Nessus will attempt to connect to every port on every system you configure it to scan. This allows it to build a detailed map of what is running on the target systems.
- For each open port it finds, Nessus will determine what service is behind that port by banner grabbing – that is, reading the service’s banner or header info. This helps identify the service.
- Once the service is fingerprinted, Nessus will conduct further probing and queries to match the service’s behavior to its database of known vulnerabilities. It is looking for signs that the target system could be exploited.
- Nessus uses techniques like SQL injection, backdoor scanning, and CGI scanning to test for the presence of thousands of common vulnerabilities.
- The scan results will list each vulnerability found and provide an assessment of the risk level (high, medium, low, for example). Nessus rates the risk based on factors like how easy it is to exploit and what access an attacker could gain.
- As Nessus doesn’t require any software on the targets, it can scan entire networks remotely very easily. Admins only need to install it on one system.
In summary, Nessus leverages port scanning to map out all services running on a target system, matches what it finds against a huge database of known vulnerabilities, and provides detailed reports on any weaknesses present that could potentially be exploited by attackers. It does this efficiently without needing to be installed on every system.
How to Install Nessus?
Nessus is a versatile cybersecurity solution comprising a server, known as “nessusd,” and a client that can be deployed on various platforms. Here’s a step-by-step guide to getting Nessus up and running:
- Download Nessus: Start by visiting the official Nessus website at www.nessus.org. There, you can find the latest release of Nessus available for Unix/Linux platforms. Download the appropriate package to your system.
- Server Installation: The Nessus server is compatible with Unix/Linux platforms, including Mac OS X and above, with developer tools installed. After downloading the Nessus package, follow the installation instructions provided on the website. During installation, you’ll be prompted to perform some quick configuration options, such as adding a user. Detailed guidance for these steps can be found at https://www.nessus.org/demo/first.html.
- Client Installation: While the Nessus server primarily supports Unix/Linux platforms, clients are available for Unix/Linux, Windows, and Mac. To download and install a Windows client, visit https://nessuswx.nessus.org/. For Unix/Linux and Mac clients, the installation process is typically included with the server installation.
Using Nessus (Part 1): Running a Scan
With Nessus successfully installed, you’re now equipped to launch scans to identify vulnerabilities in your network. Here’s how to get started:
- Run the Nessus Client: Launch the Nessus client on your chosen platform. The client interface provides essential tabs and options for configuring your scans.
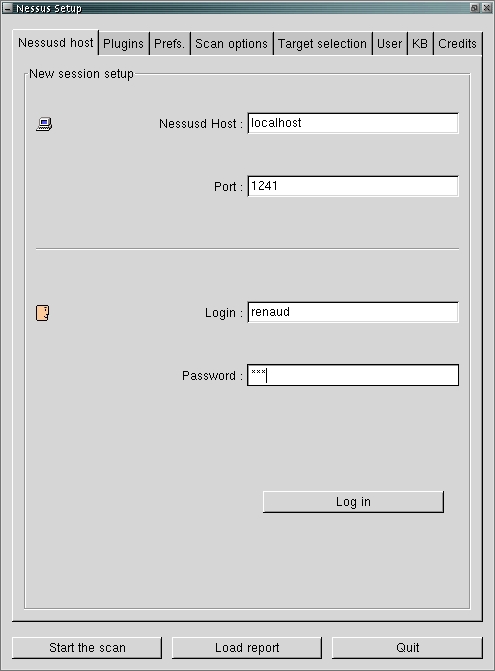
- Configure Nessusd Host: In the “Nessusd host” tab, enter the IP address of the Nessus server you wish to connect to. Additionally, provide the username and password required for authentication.
- Select Target Host(s): Navigate to the “Target Selection” tab to specify the host or hosts you want to scan. This is where you define the scope of your scan, indicating which systems will be evaluated for vulnerabilities.
- Start the Scan: Once you’ve configured the scan parameters, click the “Start the scan” button to initiate the vulnerability assessment.
Using Nessus (Part 2): Analyzing the Report
After completing a scan, Nessus clients offer powerful tools for analyzing the results:

- Review Vulnerabilities: The Nessus client typically presents a list of vulnerabilities detected during the scan. Each vulnerability is evaluated for its severity, and suggested remediation steps are often provided to help address the issues.
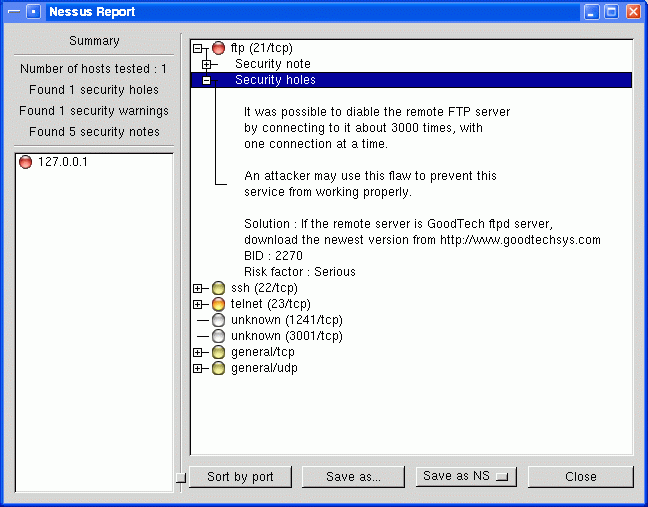
- Generate Reports: Nessus clients can produce comprehensive and graphical reports in various formats. These reports are invaluable for administrators overseeing multiple systems, as they provide an overview of the network’s security posture. You can explore examples of these reports at https://www.nessus.org/demo/third.html.
With Nessus at your disposal, you’re armed with a potent cybersecurity ally capable of identifying vulnerabilities, offering solutions, and helping you maintain the integrity of your digital assets.

Conclusion
Nessus is one of the most widely used and powerful vulnerability scanners in cybersecurity today. As cyber threats become more sophisticated, organizations must take proactive measures to identify and remediate vulnerabilities before they can be exploited by attackers.
Nessus enables automated scanning of networks, operating systems, web applications, databases, and more to detect misconfigurations, missing patches, default accounts, and other weaknesses. The detailed vulnerability reports generated by Nessus equip security teams with actionable insights to strengthen their security posture across the enterprise.
To gain hands-on experience using this essential cybersecurity tool, consider enrolling in CCS Learning Academy’s courses on ethical hacking and penetration testing. Our expert instructors will guide you through installing, configuring, and running scans with Nessus in lab environments. You’ll be able to experiment safely with different scan settings, interpret results, and practice reporting.
With CCS Learning Academy’s project-based curriculum, you’ll gain practical skills to confidently deploy Nessus in real-world cybersecurity roles. Don’t wait – register today and take the first step towards a rewarding career in cybersecurity.
FAQs


